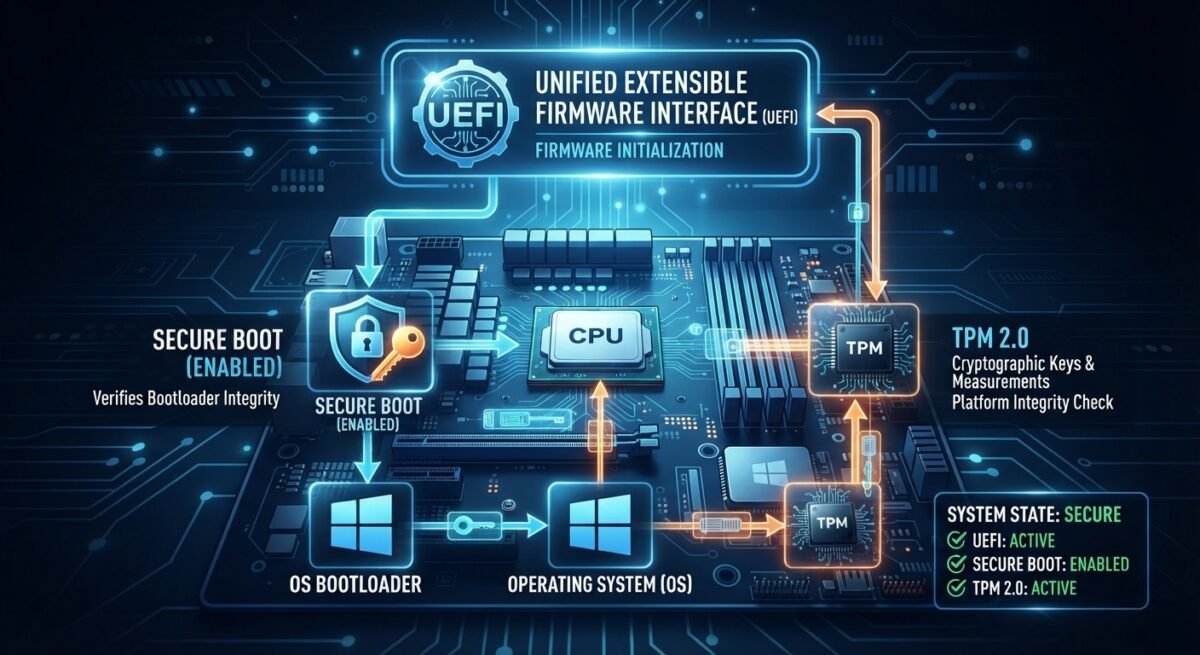
Modern computer security begins milliseconds after you press the power button—long before an operating system kernel loads, user accounts authenticate, or antivirus software initializes. For decades, personal computers relied on legacy BIOS firmware that ran in 16-bit real mode, addressed limited memory, and read executable code from a Master Boot Record without cryptographic verification. Today, three foundational technologies—UEFI, Secure Boot, and the Trusted Platform Module (TPM)—form the architectural backbone of trusted startup on modern PCs, servers, and embedded systems.